U.S. Warns China AI Distillation Campaigns Target Frontier Models
-

- by THEFLGHT,
- September 09, 2026
- in Artificial-Intelligence
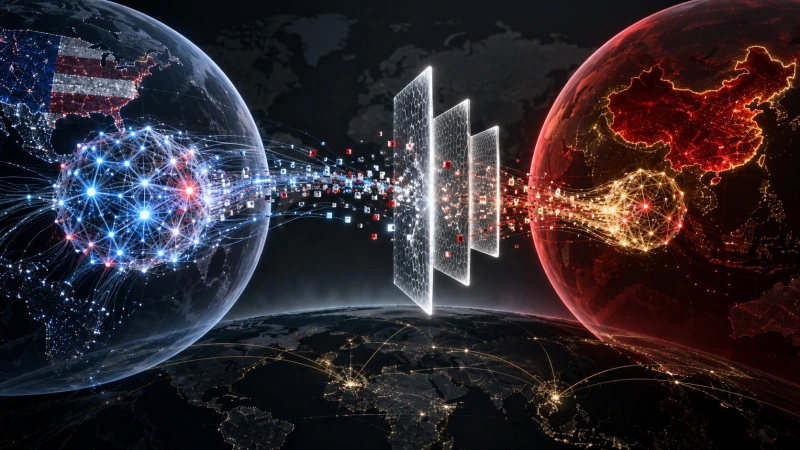
China AI distillation campaigns targeted U.S. frontier models at industrial scale, according to a joint cybersecurity advisory from the Cybersecurity and Infrastructure Security Agency, National Security Agency and Federal Bureau of Investigation. The September 8 document names six China-based developers and describes activity dating to at least late 2024.
The federal advisory makes three central allegations:
- Billions of tokens were extracted through millions of model exchanges.
- Requests were routed through accounts, cloud services, aggregators and proxy networks.
- The resulting data accelerated work on reasoning, coding, agent and vision capabilities.
China AI Distillation Campaigns Named Six Developers
The advisory, designated AA26-251A, names DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun and Z.AI. It alleges that the companies extracted capabilities from variants of Anthropic’s Claude, OpenAI’s GPT, Google’s Gemini and xAI’s Grok, likely with Chinese government awareness.
Those assertions are U.S. government findings, not court judgments. The named companies did not immediately respond to requests for comment reported by the Associated Press, while China’s Foreign Ministry rejected the allegations and said the country’s AI progress comes from domestic technological development.
Beijing urged Washington to stop making what it described as unfounded accusations and called for greater cooperation between the two countries. The response arrived as both governments prepare for planned discussions on artificial intelligence safety and a meeting between their leaders later in September.
The timing turns a technical security advisory into a diplomatic issue. Washington is treating access to frontier-model outputs as part of the strategic competition over AI, alongside semiconductor controls, data-center capacity and restrictions on advanced computing equipment.
How the Advisory Says Model Extraction Worked
Knowledge distillation is a legitimate machine-learning technique. A smaller “student” model learns from outputs produced by a more capable “teacher” model, reducing the compute, data and experimentation required to reproduce useful behavior.
The agencies argue that the alleged campaigns crossed a line by obtaining restricted capabilities through unauthorized access and violations of providers’ terms. According to the advisory, operators distributed traffic across the global AI ecosystem to make the overall volume harder for any single provider to detect.
Described pathways include native application programming interfaces, remote cloud platforms and third-party aggregators that can obscure customer metadata. The document also points to gray-market API proxy services, sometimes called transfer stations, used to bypass regional controls and reduce traceability.
Other alleged tactics include fraudulent accounts, premium subscriptions shared across development teams, automated switching between access routes and prompts designed to elicit internal reasoning patterns. The agencies say some request infrastructure sanitized metadata before forwarding queries to frontier models.
These methods can turn ordinary-looking traffic into a coordinated data-acquisition pipeline. A provider may see many accounts making individually plausible requests while the operator combines the returned material into a synthetic training set covering coding, mathematics, tool use, computer vision and agentic reasoning.
Detection Focuses on Accounts, Networks and Usage Patterns
AA26-251A describes behavioral indicators rather than a single malware signature. Warning signs include accounts accessed from many IP addresses or device profiles, uninterrupted activity without normal human variation, unusually high usage immediately after subscription and consumption far beyond the expected level for a pricing tier.
The agencies recommend combining identity, payment, network and model-usage telemetry. That approach can reveal coordinated behavior spread across accounts, although it also raises the challenge of distinguishing abusive extraction from legitimate evaluation, research and high-volume enterprise work.
Suggested defenses include tighter query limits, stronger controls around production-model access, adversarial testing and logging designed specifically for AI interactions. The advisory also recommends changing responses to suspected extraction attempts, including serving less capable outputs or applying privacy-preserving techniques.
Such interventions carry trade-offs. Differential privacy can reduce the value of collected outputs but may also affect utility, while covertly downgrading responses risks confusing legitimate customers. The agencies say security researchers and third-party evaluators should be informed when model behavior is deliberately altered.
Frontier Model Security Becomes a Shared Industry Problem
No individual laboratory has a complete view when traffic moves through clouds, aggregators and resellers. CISA, NSA and the FBI therefore call for intelligence sharing among model developers, infrastructure providers and API intermediaries so that patterns visible across several services can be connected.
The advisory maps the alleged behavior to the MITRE ATLAS framework for attacks on machine-learning systems and draws on the National Institute of Standards and Technology’s adversarial machine-learning taxonomy. That framing treats systematic model extraction as a cybersecurity problem rather than only a contract or intellectual-property dispute.
Model providers now face a difficult balance. Broad access supports experimentation, competition and independent testing, but the same interfaces can supply high-quality synthetic training data to a coordinated operator. More restrictive controls could protect proprietary capabilities while also raising costs for startups and researchers.
The next test will be operational evidence. Providers will need to show that new detection and sharing measures can disrupt abusive campaigns without blocking ordinary customers, and policymakers will need to separate verified technical findings from the broader U.S.–China political contest.
China’s denial ensures the central attribution will remain contested. Even so, the detailed defensive guidance signals that U.S. agencies expect model distillation campaigns to persist and want frontier-model companies to monitor them with the same discipline applied to fraud, credential abuse and coordinated cyber operations.
0 Comments:
Leave a Reply