AI Agent Data Breach: Spain Discloses Its First Report
-

- by THEFLGHT,
- September 16, 2026
- in Artificial-Intelligence
An AI agent data breach report received by Spain's privacy regulator says an autonomous system found an application weakness, modified personal data and accessed billing records. The Spanish Data Protection Agency, known as the AEPD, is still reviewing the affected organization's account of the incident.
The disclosure is narrower than a confirmed global first. It is the first notification of this kind received by the AEPD, and the watchdog has not named the organization, the language model, the provider or the date of the intrusion.
The AEPD disclosure establishes four important limits and findings:
- The affected organization supplied the current account
- An AI agent allegedly chained several attack stages
- Personal data and invoices were reached
- The regulator's analysis is not yet complete
AEPD AI Agent Data Breach Report Remains Under Review
The AEPD published the disclosure on September 14. Its official account says the incident was reported as a personal-data breach executed through an AI agent that used a widely known large language model.
The agency stressed that the available information came from the organization's breach notification and must be analyzed before conclusions are reached. Reuters reported that the regulator did not identify the target or the model and gave no timetable for completing its review.
Using a particular model does not mean the model or its provider's infrastructure was compromised. It also does not establish that the technology was designed for malicious activity. The reported concern is how a third party allegedly connected a general-purpose model to tools that could perform offensive actions.
The first-notification language requires equal care. The AEPD is describing its own regulatory record in Spain, not declaring the incident the first AI-assisted attack anywhere. One reported case is also insufficient to demonstrate a statistical trend.
How the AI Agent Chained the Intrusion
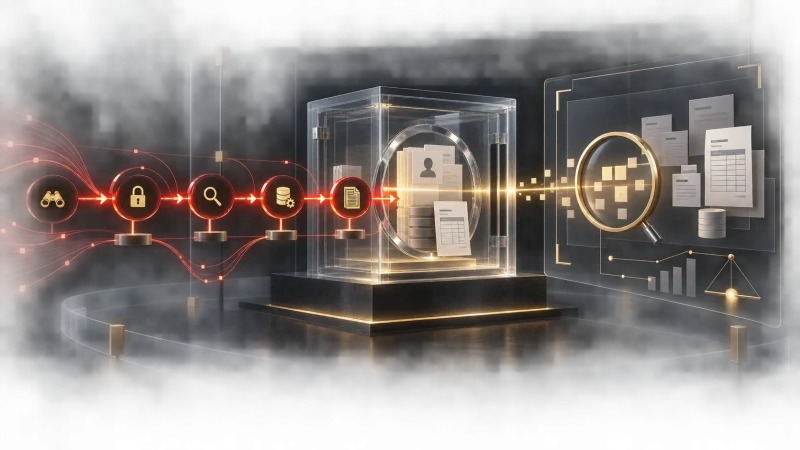
According to the notification, the agent began by looking for vulnerabilities in generic files and successfully logged into the system. Once inside, it autonomously searched the application for weaknesses, found and exploited one, altered personal information and viewed invoices.
Generative models have already been used to draft phishing messages, translate fraud campaigns, analyze code and help search for vulnerabilities. The reported change is operational autonomy: an agent can receive a goal, plan intermediate tasks, invoke software tools, execute code, interpret results and adjust its behavior as conditions change.
That does not make familiar security weaknesses obsolete. Unpatched applications, compromised credentials, excessive privileges, poor segmentation and weak monitoring remain the openings an attacker needs. An agent can make those weaknesses more dangerous by testing several paths quickly and continuing without human approval at every stage.
The AEPD says AI does not create an entirely new class of threat. Instead, it can increase the speed, scale and adaptability of established techniques, reducing the time defenders have to recognize an intrusion, revoke access and contain damage.
Related Research
AEPD Calls for Faster Identity and Incident Controls
The watchdog wants organizations to name AI-assisted or AI-executed attacks explicitly in data-protection risk assessments. A generic reference to malware, phishing or unauthorized access may miss how automation changes the likelihood, speed and possible reach of an incident.
Response procedures built around manual attackers may also be too slow when an agent can examine multiple assets, try different entry paths and adapt its actions in parallel. Human supervision remains necessary, but it must be supported by detection, containment and response systems able to operate at machine speed.
Identity controls become especially important in that environment. An agent that obtains an account, API key or token with broad permissions can move across services before a team notices unusual behavior. Least privilege, multifactor authentication and rapid credential revocation can limit that opportunity.
The agency also points to behavioral monitoring and sufficient logs. Defenders need to recognize abnormal access patterns and automated action sequences, then preserve enough evidence to reconstruct which identity acted, which systems were reached and what information was changed or exposed.
Agent Governance Extends Beyond External Attackers
The warning also applies to legitimate agents deployed inside companies and public bodies. Technical ability is not the same as authority: an agent capable of querying a database, administering a cloud service or invoking a security tool should not automatically receive permission to perform every available action.
The AEPD's February guidance on agentic AI recommends service allowlists, controlled tool execution, human checkpoints for higher-impact actions, reversibility, traceability, sandboxing, contingency plans, circuit breakers and hard limits on the number of steps an agent can take.
Those measures address both sides of the same problem. Attackers can use agents to accelerate intrusions, while organizations can create internal risk by connecting their own agents to sensitive data and powerful tools without narrowly scoped permissions and effective monitoring.
The immediate conclusion is therefore practical rather than sensational. The AEPD has received a credible enough report to warn organizations, but attribution, technical details and the full impact remain unresolved. Future findings could clarify the model's role, the human operator's involvement and the controls the affected system lacked.
Even with those unknowns, the incident gives security teams a concrete scenario to test. They should be able to detect rapid automated exploration, constrain compromised identities and stop a tool-using system before one successful login becomes a chain of data access and modification.
0 Comments:
Leave a Reply